Methodology
A disciplined approach. Real-world results.
Our methodology pairs experienced, human-led testers with proven practice and rigorous validation. The exact workflow is adapted to scope, technology, risk, and rules of engagement.
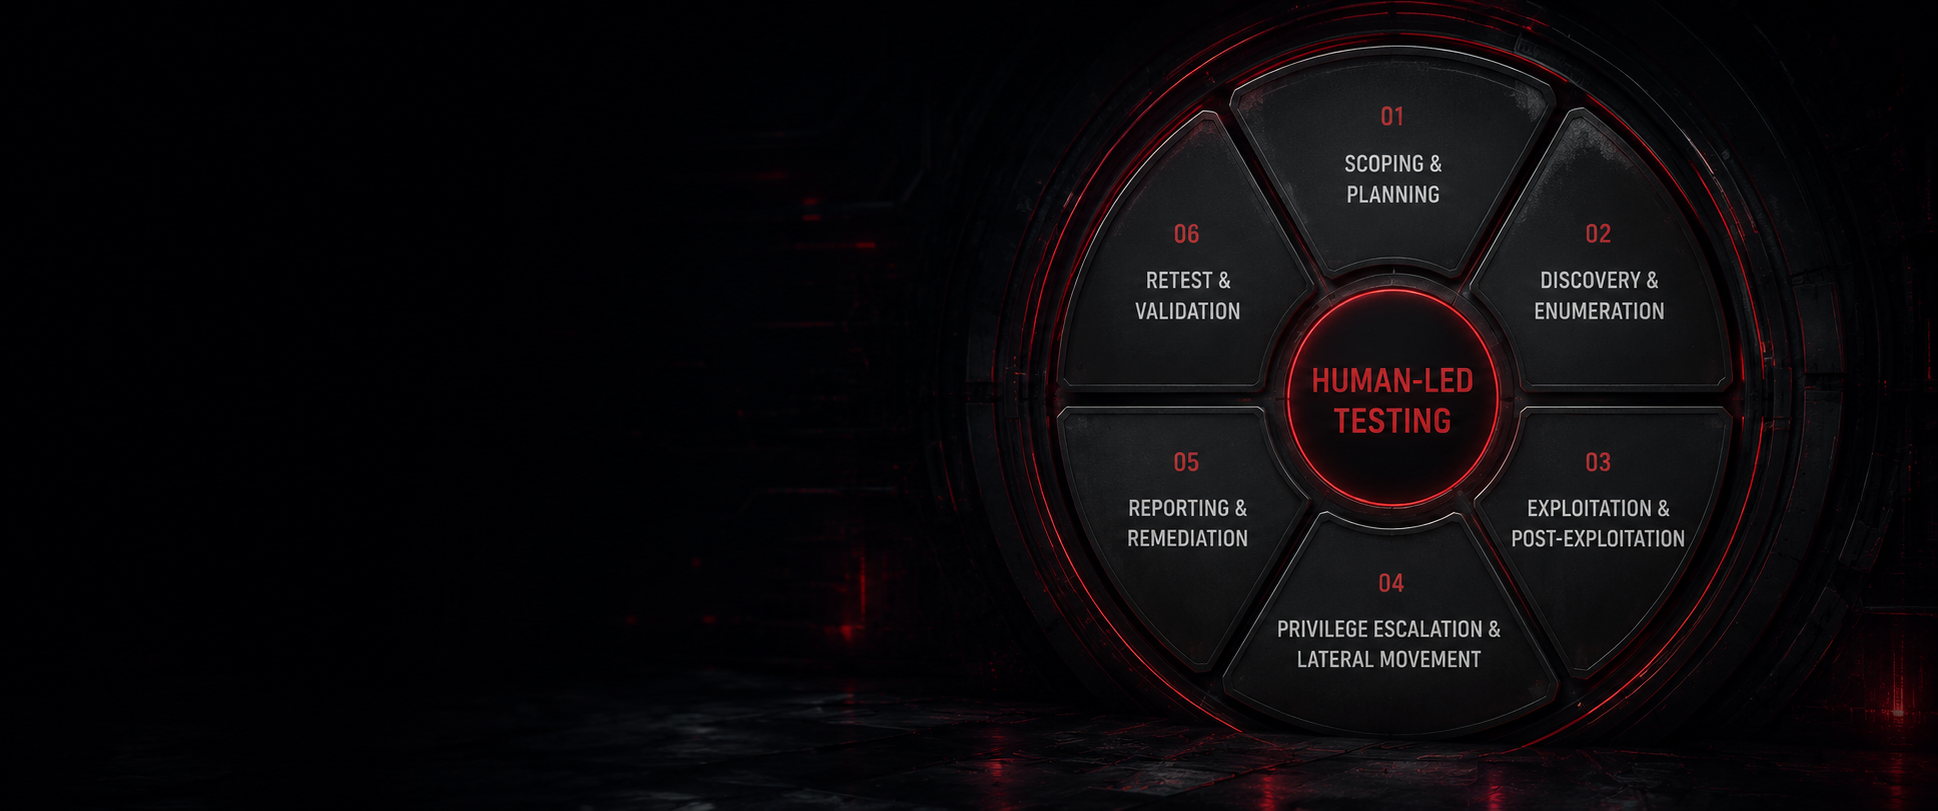
How an engagement runs
Human-led at every stage — the sequence adapts to each engagement.
- 01
Scoping & Planning
Define objectives, boundaries, rules of engagement, and success criteria together with your team.
- 02
Discovery & Enumeration
Map the attack surface and enumerate assets, services, and potential entry points.
- 03
Exploitation & Post-Exploitation
Controlled exploitation of validated weaknesses, where in scope, to demonstrate real impact.
- 04
Privilege Escalation & Lateral Movement
Where achievable, escalate privileges and move laterally to map realistic attack paths.
- 05
Reporting & Remediation
Clear, evidence-backed findings with business impact and prioritized, practical remediation.
- 06
Retest & Validation
Validate fixes and confirm that identified issues have been properly addressed.
How we work
-
Human-Led Testing
Experienced testers, manual depth, and creative thinking — not just automated scans.
-
Evidence-Driven Findings
Every finding is backed by clear, reproducible evidence.
-
Controlled Execution
Testing is performed carefully and within agreed rules of engagement.
-
Actionable Remediation
Guidance you can act on, mapped to business impact and priority.
Methodical. Thorough. Human-led.
That's how we deliver real security.