Agentic AI Security
Security testing for systems that can act.
Traditional applications execute deterministic code paths. Agentic systems introduce new trust boundaries between models, tools, data, infrastructure, other agents, and the humans who direct them — and each boundary is something to test.
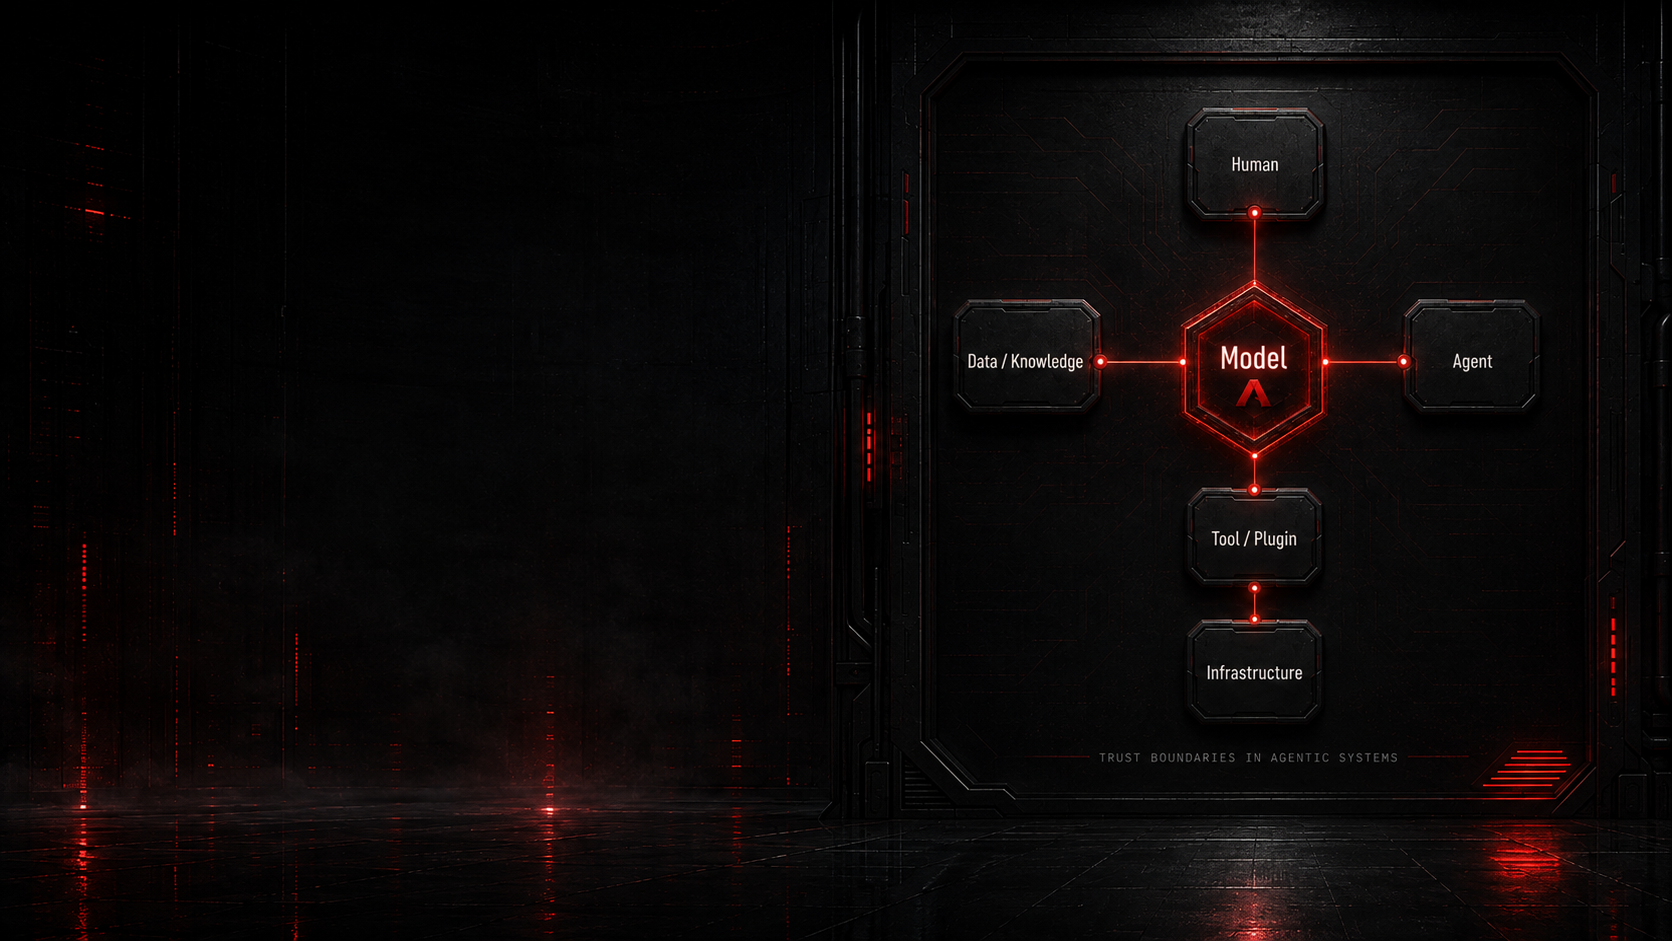
What we assess
-
Agent Authorization Boundaries
What an agent is permitted to do, and whether those limits hold under adversarial input.
-
Tool-Use Security
How tools and functions are exposed, invoked, and constrained.
-
Prompt & Context Manipulation
Resistance to prompt injection and untrusted context influencing behavior.
-
Data Exposure
Sensitive data reachable through prompts, tools, retrieval, or outputs.
-
RAG / Retrieval Trust
Trust placed in retrieved content and its influence on decisions.
-
MCP / Tool Integration
Security of Model Context Protocol and tool-integration surfaces.
-
Agent-to-Agent Workflows
Trust, delegation, and communication between cooperating agents.
-
Human Approval Controls
Human-in-the-loop approvals and safety gates, and how they can be bypassed.
Emerging technology. Real-world risk.
Let's test your agentic systems.